India (GNP): A ransomware group has published a large cache of files linked to India’s largest nuclear power plant on the dark web, including purported facility blueprints and supplier records, as contractor Reliance Group confirmed a partial data breach tied to the project.
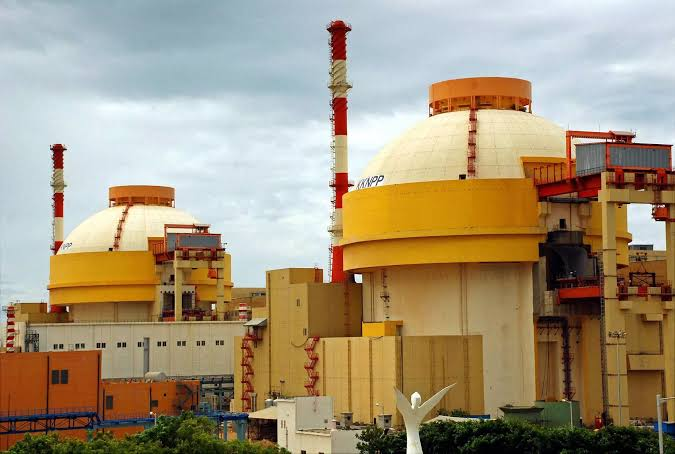
The Kudankulam Nuclear Power Plant, located in the southern state of Tamil Nadu, is India’s largest atomic energy facility and central to Prime Minister Narendra Modi’s plans to expand the country’s nuclear power capacity. The ransomware group, identified as World Leaks, posted documents it attributed to the Reliance Group, including blueprints of parts of the plant, supplier information, inspection records and insurance documents. The authenticity of the files has not been independently verified.
Reliance Group, one of the contractors involved in the project, acknowledged a partial breach of data stored on a server hosted by Indian data center provider Yotta, saying the Indian government had been informed. The company did not disclose the specific information compromised.
A source familiar with the matter said the Nuclear Power Corporation of India has been coordinating with Reliance over the incident, while the Indian Computer Emergency Response Team is investigating. Yotta said it detected suspicious activity on a server belonging to Reliance Infrastructure on May 29 and immediately terminated the activity, describing the move as having prevented a suspected ransomware execution.
The company said Reliance later informed it that external threat actors had claimed responsibility for a breach, adding that it could not independently verify those claims but had shared its technical investigation findings with Reliance and was assisting the ongoing inquiry. India’s Department of Atomic Energy and the Nuclear Power Corporation of India have not publicly commented on the reported breach.
The leaked cache reportedly contains approximately 19,000 sensitive files selected from more than 858,000 files allegedly stolen from Reliance. Among the documents are purported blueprints of ventilation and cooling systems for the plant’s Units 3 and 4, floor layouts of a common control room, supplier lists, equipment inspection records and insurance policies. One document reportedly outlines a $112 million insurance policy covering terrorist attacks affecting the two reactor units, which remain under construction and are expected to become operational by 2027.
Also Read: Bangkok Pub Fire Death Toll Rises to 32 as Negligence Probe Widens
Security experts said the leaked files do not appear to include information on the reactors’ core systems, which are supplied by Russia’s state-owned Rosatom, but cautioned that the documents could still expose critical support infrastructure and supply chains. Nickolas Roth, senior director at the Nuclear Threat Initiative, said such information could allow hostile actors to identify suppliers, map facility support systems and assess potential security vulnerabilities.
The breach adds to growing cybersecurity concerns in India, where data breaches have become increasingly frequent. Cybersecurity firm Surfshark reported that India recorded nearly 28.9 million compromised accounts last year, ranking third globally behind the United States and France. The Kudankulam plant was previously linked to a cybersecurity incident in 2019, when malware associated with a North Korean hacking group was detected on its administrative network; Indian authorities said at the time that the plant’s operational systems were not affected.

Managing Editor at Global News Pakistan (GNP), with a Bachelor's degree in International Relations from Riphah International University, graduated with a Gold Medal. Reach out at sabahtareengnp@gmail.com